
Studio Audit Explorer
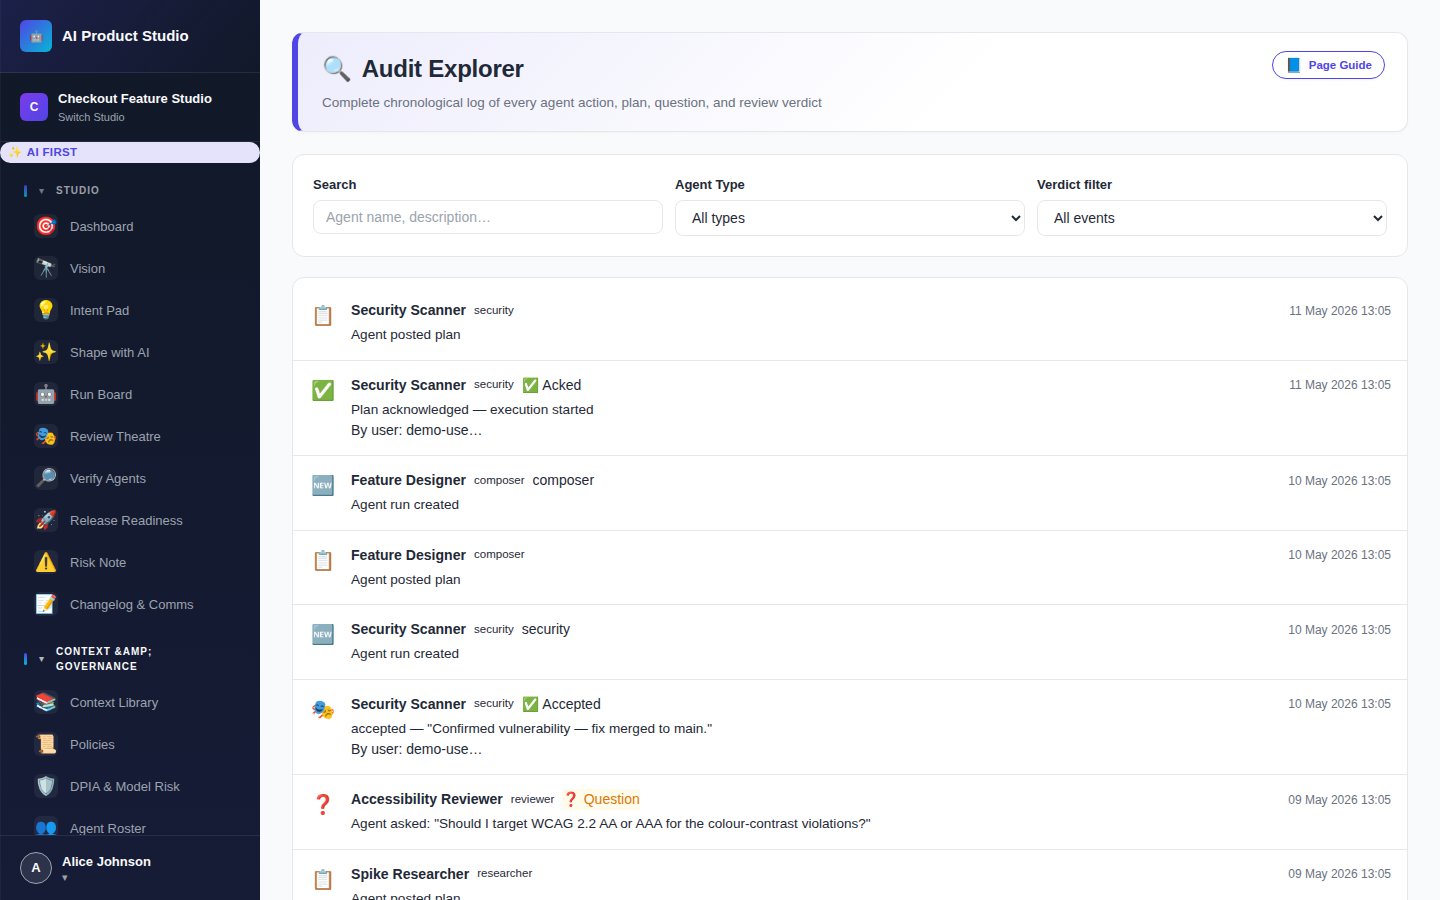
The Audit Explorer provides an immutable, append-only record of every governance-significant action in the Studio — from plan approvals to release sign-offs — with named actors and precise timestamps.
What is audited
Filtering and export
Filter by date range, actor, event type, run ID, intent ID, or release ID. Export filtered results as CSV or JSON for external compliance review or incident investigation.
Change log
Studio owners and admins also see the studio’s Change log on this page: the server’s audit of every audited change, field by field, newest first. Show older changes reads further back. Export JSON downloads it; a very large log is exported in parts, and each export is itself recorded in the log.
Append-only
Audit entries are written to a store the application can add to but cannot change or delete from — that is enforced on the application’s own access rights, not by a setting anyone in a workspace, studio or organisation can alter. Entries are kept for the audit retention period.
The audit log records what changed. What was checked before work moved — each gate decision, exception and approval, with a chain that shows if any is missing — is the evidence ledger behind each work package’s and release’s Passport. See Artefact Passport & Evidence Ledger.