
Studio Policies
Policies are configurable rules that govern agent behaviour, code quality standards, and disclosure requirements for AI-generated content in your Studio.
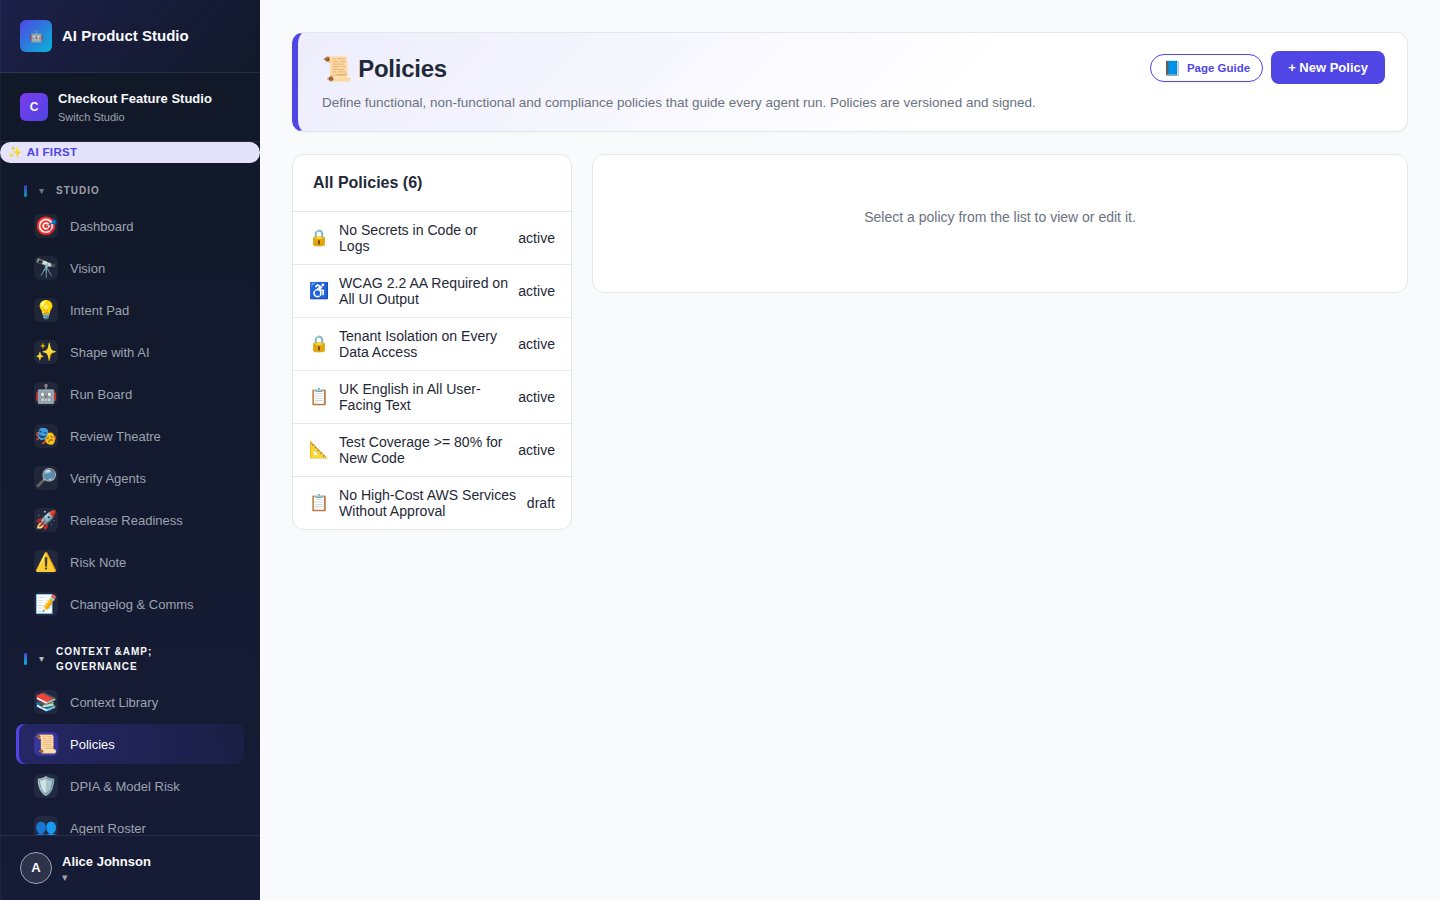
Built-in policy categories
Security Baseline — Requires Security agent sign-off before any code affecting authentication, authorisation, data access, or external integrations is released.
Accessibility Standard — Requires WCAG 2.2 AA compliance check on all UI-affecting changes.
AI Disclosure — Mandates that all AI-generated content is labelled with AI-origin badges in the codebase and documentation.
Test Coverage — Minimum test coverage threshold (configurable, default 80%) required before release.
Dependency Audit — Blocks release if newly introduced dependencies have known high or critical CVEs.
Data Minimisation — Flags any intent or output that appears to collect or process personal data without explicit justification.
Custom policies
Create organisation-specific policies using the policy builder. Define trigger conditions (e.g. "when agent type is Coder and files in src/api/ are modified"), required checks, and enforcement mode (block vs. warn).
Enforcement modes
- Block: Policy violation prevents release creation. Must be resolved or formally excepted.
- Warn: Violation is flagged in the release summary but does not block. Approver must acknowledge.
- Audit: Violation is recorded in the audit trail but no action is required at release time.